Google is taking the classic business wedge approach. Find a market that is making good money and is related to another market that might make money in the future; then launch a product into the market that's making money and expand into the one that might make money later.
Google can immediately grab some low hanging fruit by approaching businesses first. Their rates for merchant transactions are a full 1% point less than PayPal for all businesses except those doing more than $100,000/mo in processing. They're basically offering the processing near cost and using the service to expand AdWords revenue.
From a business standpoint, that's a terrifically smart thing since their primary profits come from advertising sales and investors will want to see those sales continue to expand.
For business customers, this is also a watershed event. Hopefully it will force PayPal and the regular credit card merchant account providers to reduce their internet transaction fees. The average merchant fee for small and medium sized businesses accepting credit cards through a company like Authorize.net is 2.35% + $.35-50 cents per transaction + a $20/mo gateway fee and a $25/mo minimum processing fee.
Small businesses wanting to sell stuff online should be all over Google's offering. It's cheaper than their bank and cheaper than PayPal. Plus they will see the AdWords thing as free advertising since they'd have to spend that money on the credit card processing fees regardless. So the deal works well in favor of small businesses.
Later, I can see Google expanding and testing the waters with person-to-person micropayments. That market is pretty much non-existent (in terms of a percentage basis) here in the US. Outside the US there is more interest but even in those places it's still in limited stages of use.
For the micropayments business to work here in the US, however, there have to be some fundamental changes to the way the banking system works. The fees to get money on and off of ATM, debit and credit cards are still too high to make business cases involving the handling of large numbers of tiny transactions profitable. Just as any small quick service restaurant (like local sandwich shop) who takes credit cards... they'll tell you how bad it hurts to lose nearly 2% of the bill plus 30-50 cents of every transaction to fees. That's why in many of them you'll see a sign asking credit/debit card users to please make a purchase of at least $5-10 when paying with their cards.
}Davoice
Friday, June 30, 2006
Saturday, June 24, 2006
Skype with a Windigo powered USB dongle & BT headset
OK, so I ventured off into the world of Skype recently. Here's the first thing I learned: Bluetooth headsets on Windows XP SP2 suck.
But all is not lost. I finally cracked the code on my particular combination.
What I'm using:
Motorola HS820 Bluetooth Headset
Cyber-Blue Bluetooth EDR v2.0 Dongle
 I first tried using it with the included software which comes on a little mini-CD with virtually no identification. It just says Bluetooth and V2.0 on the CD. No company name identification, no nothing. You can see that CD and the dongle over to the right.
The software on the CD sort of worked but not really. It worked backwards with Skype. When you connected the headset and it was ready to talk, upon dialing a Skype call it would disconnect. How annoying!
Then I tried switching to Microsoft's Bluetooth drivers. What a crock that was. That was when I learned that in their infinite wisdom, Microsoft does not support the headset profile in their Bluetooth drivers. How sucky is that?
Cyber-Blue's website was useless. They're an OEM and this unit is just their generic house model that's sold cheap. (What was I expecting from a $9 purchase at Geeks.com?) They don't have any supporting files or anything on their site.
So, then I figured I'd check out the software provider's website - Windigo Systems. Linked from their homepage is a Support page. On that page they provide "Blue Manager 3.1c". Well that would be great except for the fact that what I had on the CD that came w/ the dongle was 3.2b and I certainly wasn't going to chance using even older software.
Off to the Google I went again. I found few references to Blue Manager software. The only thing I found was another OEM who was offering Blue Manager 3.3 if you used a form to request it - problem being that you had to own one of their devices and report it's serial number to get the software. Stinkie.
Back to Windigo I go. This time I noticed they had a support email address listed. "What the heck" I figured. At least I'll have spent $9 and tried. To my amazement I got an email back in about 4 hours with a link to Blue Manager version 3.4d. Now why didn't they have that linked to their support page to begin with!?! Oh well. At least they were nice enough to email me back (in broken English, so I assume they're staffed with native Asian speakers so they can work w/ their Chinese and southeast Asian manufacturing partners).
For some reason I was unable to download anything from their website w/o getting a notice from my unzip program that there was a CRC error and the file was corrupt. Poey. But I was able to download it to my office PC (thanks to Logmein) and FTP it to myself w/o problem. I still have no clue why I wasn't able to download it over my Sprint/Embarq DSL connection. No matter, I had the software now. There was no stopping me. Or so I thought.
I begin to run the software. It wants to uninstall all the old software. Kaboom. BSOD! Yep, a nice blue screen of death. So I unplug the USB dongle and reboot. The second time I ran the software it wanted to uninstall the old software, so I let it try again. No BSOD that time. Oh, but it required the obligatory reboot before it could finish. I let it reboot then started the installer again (manually b/c it wasn't smart enough to start itself back up). Now the real install begins. It gets 3/4 of the way through the install and it tells me it can't finish without my Bluetooth dongle being plugged in. So I plug it in. Windows installs it again from scratch as if it were a new piece of hardware. Kaboom. BSOD AGAIN! Bollucks!
Ok, so I reboot with the dongle attached this time. Windows seems happy when it comes back up. I have the nice Microsoft Bluetooth icon in the system tray. I start the Blue Manager 3.4d installer again. I am asked by the software if I want to install the COM port for VoIP and data or for VoIP only. Since I don't have a Bluetooth capable phone yet, I go with VoIP only. The installer chugs along. It gets all the way through this time and the Microsoft Bluetooth icon disappears. That's the signal that Blue Manager has taken over control. Oh but wait... the software needs to reboot my computer again.
So... here were are 5 reboots later - 2 of which were planned. The software appears to have successfully installed that last time. I am able to start Blue Manager for Skype. Joy, it's a 2 step process to start Blue Manager so you can use your headset. Instead of automatically starting when Windows does - there's not even an option for that - you have to start Blue Manager for Skype and THEN start Blue Manager 4.3d so you can actually use the headset. Annoying but livable.
 I put my Motorola HS820 into pairing mode (how stupid were the Motorola engineers for putting every single function on this thing except volume - and I bet they tried that in development! - under the control of the single button!). If you don't master counting your button hold time, you're destined for failure. Then I started the discovery process in Blue Manager by hitting Refresh. After entering the pairing password - "0000" - they paired. Yippie.
Now for the real test. Can I make a Skype call. It took a little fiddling b/c the new Blue Manager 3.4d software did not automatically set the headset as the audio device in Skype. To do that, in Skype go to Tools -> Options and set Windigo Audio BT device as the default for your incoming and outgoing audio. Once that was done, I was able to just hit the button on the Motorola HS820 and Blue Manager kept a connection open to the headset. It even kept the connection open after I hung up the Skype call.
All is not perfect in this arrangement. I can't use the button on the headset to answer or disconnect a Skype call like you can on a cell phone. You have to acknowledge the call using the keyboard and mouse as always. And if you forget to connect the headset by pressing the button before you answer the call neither party can hear anything.
The good news is that battery life for the Motorola HS820 is about 6 hours of talk time. So it's possible to just connect the headset while you're sitting at the PC and leave it connected. That also helps with knowing when calls are coming in. Unless you set the Skype option to "Ring PC speaker on incoming call" you won't hear anything to let you know a call is coming in if you'd forgotten to "connect" your headset or if the Bluetooth connection dropped (in cases like when you left the PC to go to the bathroom w/o taking the headset off).
Hopefully Skype will get a clue and help these headset folks or Microsoft get a grip on Bluetooth headsets. They way the work now is manageable. But most definitely not optimal.
}Davoice
But all is not lost. I finally cracked the code on my particular combination.
What I'm using:
Motorola HS820 Bluetooth Headset
Cyber-Blue Bluetooth EDR v2.0 Dongle
I first tried using it with the included software which comes on a little mini-CD with virtually no identification. It just says Bluetooth and V2.0 on the CD. No company name identification, no nothing. You can see that CD and the dongle over to the right.The software on the CD sort of worked but not really. It worked backwards with Skype. When you connected the headset and it was ready to talk, upon dialing a Skype call it would disconnect. How annoying!
Then I tried switching to Microsoft's Bluetooth drivers. What a crock that was. That was when I learned that in their infinite wisdom, Microsoft does not support the headset profile in their Bluetooth drivers. How sucky is that?
Cyber-Blue's website was useless. They're an OEM and this unit is just their generic house model that's sold cheap. (What was I expecting from a $9 purchase at Geeks.com?) They don't have any supporting files or anything on their site.
So, then I figured I'd check out the software provider's website - Windigo Systems. Linked from their homepage is a Support page. On that page they provide "Blue Manager 3.1c". Well that would be great except for the fact that what I had on the CD that came w/ the dongle was 3.2b and I certainly wasn't going to chance using even older software.
Off to the Google I went again. I found few references to Blue Manager software. The only thing I found was another OEM who was offering Blue Manager 3.3 if you used a form to request it - problem being that you had to own one of their devices and report it's serial number to get the software. Stinkie.
Back to Windigo I go. This time I noticed they had a support email address listed. "What the heck" I figured. At least I'll have spent $9 and tried. To my amazement I got an email back in about 4 hours with a link to Blue Manager version 3.4d. Now why didn't they have that linked to their support page to begin with!?! Oh well. At least they were nice enough to email me back (in broken English, so I assume they're staffed with native Asian speakers so they can work w/ their Chinese and southeast Asian manufacturing partners).
For some reason I was unable to download anything from their website w/o getting a notice from my unzip program that there was a CRC error and the file was corrupt. Poey. But I was able to download it to my office PC (thanks to Logmein) and FTP it to myself w/o problem. I still have no clue why I wasn't able to download it over my Sprint/Embarq DSL connection. No matter, I had the software now. There was no stopping me. Or so I thought.
I begin to run the software. It wants to uninstall all the old software. Kaboom. BSOD! Yep, a nice blue screen of death. So I unplug the USB dongle and reboot. The second time I ran the software it wanted to uninstall the old software, so I let it try again. No BSOD that time. Oh, but it required the obligatory reboot before it could finish. I let it reboot then started the installer again (manually b/c it wasn't smart enough to start itself back up). Now the real install begins. It gets 3/4 of the way through the install and it tells me it can't finish without my Bluetooth dongle being plugged in. So I plug it in. Windows installs it again from scratch as if it were a new piece of hardware. Kaboom. BSOD AGAIN! Bollucks!
Ok, so I reboot with the dongle attached this time. Windows seems happy when it comes back up. I have the nice Microsoft Bluetooth icon in the system tray. I start the Blue Manager 3.4d installer again. I am asked by the software if I want to install the COM port for VoIP and data or for VoIP only. Since I don't have a Bluetooth capable phone yet, I go with VoIP only. The installer chugs along. It gets all the way through this time and the Microsoft Bluetooth icon disappears. That's the signal that Blue Manager has taken over control. Oh but wait... the software needs to reboot my computer again.
So... here were are 5 reboots later - 2 of which were planned. The software appears to have successfully installed that last time. I am able to start Blue Manager for Skype. Joy, it's a 2 step process to start Blue Manager so you can use your headset. Instead of automatically starting when Windows does - there's not even an option for that - you have to start Blue Manager for Skype and THEN start Blue Manager 4.3d so you can actually use the headset. Annoying but livable.
I put my Motorola HS820 into pairing mode (how stupid were the Motorola engineers for putting every single function on this thing except volume - and I bet they tried that in development! - under the control of the single button!). If you don't master counting your button hold time, you're destined for failure. Then I started the discovery process in Blue Manager by hitting Refresh. After entering the pairing password - "0000" - they paired. Yippie.Now for the real test. Can I make a Skype call. It took a little fiddling b/c the new Blue Manager 3.4d software did not automatically set the headset as the audio device in Skype. To do that, in Skype go to Tools -> Options and set Windigo Audio BT device as the default for your incoming and outgoing audio. Once that was done, I was able to just hit the button on the Motorola HS820 and Blue Manager kept a connection open to the headset. It even kept the connection open after I hung up the Skype call.
All is not perfect in this arrangement. I can't use the button on the headset to answer or disconnect a Skype call like you can on a cell phone. You have to acknowledge the call using the keyboard and mouse as always. And if you forget to connect the headset by pressing the button before you answer the call neither party can hear anything.
The good news is that battery life for the Motorola HS820 is about 6 hours of talk time. So it's possible to just connect the headset while you're sitting at the PC and leave it connected. That also helps with knowing when calls are coming in. Unless you set the Skype option to "Ring PC speaker on incoming call" you won't hear anything to let you know a call is coming in if you'd forgotten to "connect" your headset or if the Bluetooth connection dropped (in cases like when you left the PC to go to the bathroom w/o taking the headset off).
Hopefully Skype will get a clue and help these headset folks or Microsoft get a grip on Bluetooth headsets. They way the work now is manageable. But most definitely not optimal.
}Davoice


Tuesday, June 20, 2006
The coffee revolution has begun.
No Measuring, No Mess, No Wait. Just fill the tank, place a javapod™ or teapod™ in the pod holder and in less than a minute experience a gourmet cup of coffee. Regardless of cup size, the interchangeable spouts provide a seamless transition between your favorite cups.
Friday, June 09, 2006
Thursday, June 08, 2006
Feds Bust Major VoIP Scam
Duo made millions off of hacked VoIP deal
The New York Times is running an interesting story on two men who operated an Internet voice scheme that netted them more than a million in connection fees. It began with the men starting two smaller VoIP companies, and buying wholesale voice access.
The New York Times is running an interesting story on two men who operated an Internet voice scheme that netted them more than a million in connection fees. It began with the men starting two smaller VoIP companies, and buying wholesale voice access.
"Instead of buying access to other networks to connect his clients' calls, Mr. Pena paid about $20,000 to Robert Moore, the man arrested in Spokane, to create "what amounted to 'free' routes by surreptitiously hacking into the computer networks" of unwitting Internet phone providers, and then routing his customers' calls over those providers' systems, according to the federal complaint.The scam left more than 15 Internet phone companies with connectivity bills up to $300,000 each, without any revenue to show for it.
Monday, May 08, 2006
Gone in 60 seconds--the high-tech version
By Robert Vamosi
Let's say you just bought a Mercedes S550--a state-of-the-art, high-tech vehicle with an antitheft keyless ignition system.
After you pull into a Starbucks to celebrate with a grande latte and a scone, a man in a T-shirt and jeans with a laptop sits next to you and starts up a friendly conversation: "Is that the S550? How do you like it so far?" Eager to share, you converse for a few minutes, then the man thanks you and is gone. A moment later, you look up to discover your new Mercedes is gone as well.
Now, decrypting one 40-bit code sequence can not only disengage the security system and unlock the doors, it can also start the car--making the hack tempting for thieves. The owner of the code is now the true owner of the car. And while high-end, high-tech auto thefts like this are more common in Europe today, they will soon start happening in America. The sad thing is that manufacturers of keyless devices don't seem to care.
Wireless or contactless devices in cars are not new. Remote keyless entry systems--those black fobs we all have dangling next to our car keys--have been around for years. While the owner is still a few feet away from a car, the fobs can disengage the auto alarm and unlock the doors; they can even activate the car's panic alarm in an emergency.
First introduced in the 1980s, modern remote keyless entry systems use a circuit board, a coded radio-frequency identification (RFID) technology chip, a battery and a small antenna. The last two are designed so that the fob can broadcast to a car while it's still several feet away.
The RFID chip in the key fob contains a select set of codes designed to work with a given car. These codes are rolling 40-bit strings: With each use, the code changes slightly, creating about 1 trillion possible combinations in total. When you push the unlock button, the keyfob sends a 40-bit code, along with an instruction to unlock the car doors. If the synced-up receiver gets the 40-bit code it is expecting, the vehicle performs the instruction. If not, the car does not respond.
A second antitheft use of RFID is for remote vehicle immobilizers. These tiny chips, embedded inside the plastic head of the ignition keys, are used with more than 150 million vehicles today. Improper use prevents the car's fuel pump from operating correctly. Unless the driver has the correct key chip installed, the car will run out of fuel a few blocks from the attempted theft. (That's why valet keys don't have the chips installed; valets need to drive the car only short distances.)
One estimate suggests that since their introduction in the late 1990s, vehicle immobilizers have resulted in a 90 percent decrease in auto thefts nationwide.
But can this system be defeated? Yes.
Keyless ignition systems allow you the convenience of starting your car with the touch of a button, without removing the chip from your pocket or purse or backpack. Like vehicle immobilizers, keyless ignition systems work only in the presence of the proper chip. Unlike remote keyless entry systems, they are passive, don't require a battery and have much shorter ranges (usually six feet or less). And instead of sending a signal, they rely on a signal being emitted from the car itself.
Given that the car is more or less broadcasting its code and looking for a response, it seems possible that a thief could try different codes and see what the responses are. Last fall, the authors of a study from Johns Hopkins University and the security company RSA carried out an experiment using a laptop equipped with a microreader. They were able to capture and decrypt the code sequence, then disengage the alarm and unlock and start a 2005 Ford Escape SUV without the key. They even provided an online video of their "car theft."
But if you think that such a hack might occur only in a pristine academic environment, with the right equipment, you're wrong.
Real-world examples
Meet Radko Soucek, a 32-year-old car thief from the Czech Republic. He's alleged to have stolen several expensive cars in and around Prague using a laptop and a reader. Soucek is not new to auto theft--he has been stealing cars since he was 11 years old. But he recently turned high-tech when he realized how easily it could be done.
Ironically, what led to his downfall was his own laptop, which held evidence of all his past encryption attempts. With a database of successful encryption strings already stored on his hard drive, he had the ability to crack cars he'd never seen before in a relatively short amount of time.
And Soucek isn't an isolated example. Recently, soccer player David Beckham had not one, but two, antitheft-engineered BMW S5 SUVs stolen. The most recent theft occurred in Madrid, Spain. Police believe an auto theft gang using software instead of hardware pinched both of Beckham's BMWs.
How a keyless car gets stolen isn't exactly a state secret--much of the required knowledge is Basic Encryption 101. The authors of the Johns Hopkins/RSA study needed only to capture two challenge-and-response pairs from their intended target before cracking the encryption.
In an example from the paper, they wanted to see if they could swipe the passive code off the keyless ignition device itself. To do so, the authors simulated a car's ignition system (the RFID reader) on a laptop. By sitting close to someone with a keyless ignition device in his pocket, the authors were able to perform several scans in less than one second without the victim knowing. They then began decrypting the sampled challenge-response pairs. Using brute-force attack techniques, the researchers had the laptop try different combinations of symbols until they found combinations that matched. Once they had the matching codes, they could then predict the sequence and were soon able to gain entrance to the target car and start it.
In the case of Beckham, police think the criminals waited until he left his car, then proceeded to use a brute-force attack until the car was disarmed, unlocked and stolen.
Hear no evil, speak no evil
The authors of the Johns Hopkins/RSA study suggest that the RFID industry move away from the relatively simple 40-bit encryption technology now in use and adopt a more established encryption standard, such as the 128-bit Advanced Encryption Standard (AES). The longer the encryption code, the harder it is to crack.
The authors concede that this change would require a higher power consumption and therefore might be harder to implement; and it wouldn't be backward-compatible with all the 40-bit ignition systems already available.
The authors also suggest that car owners wrap their keyless ignition fobs in tin foil when not in use to prevent active scanning attacks, and that automobile manufacturers place a protective cylinder around the ignition slot. This latter step would limit the RFID broadcast range and make it harder for someone outside the car to eavesdrop on the code sequence.
Unfortunately, the companies making RFID systems for cars don't think there's a problem. The 17th annual CardTechSecureTech conference took place this past week in San Francisco, and CNET News.com had an opportunity to talk with a handful of RFID vendors. None wanted to be quoted, nor would any talk about 128-bit AES encryption replacing the current 40-bit code anytime soon. Few were familiar with the Johns Hopkins/RSA study we cited, and even fewer knew about keyless ignition cars being stolen in Europe.
Even Consumer Reports acknowledges that keyless ignition systems might not be secure enough for prime time, yet the RFID industry adamantly continues to whistle its happy little tune. Until changes are made in the keyless systems, any car we buy will definitely have an ignition key that can't be copied by a laptop.
Monday, March 20, 2006
What king of weather are you?
| You Are Sunshine |
 Soothing and calm You are often held up by others as the ideal But too much of you, and they'll get burned You are best known for: your warmth Your dominant state: connecting |
Saturday, February 25, 2006
DANGER: Your internet freedoms are on death row.
Network neutrality, a principle that ensures the free flow of ideas online, appears dead on arrival in Washington as big media once again wield influence over our elected politicians.
The numbers tell the story. According to the Center for Responsive Politics, AT&T and other telephone and cable companies are among the top contributors to the re-election campaigns of a number of house Telecommunications Subcommittee members, including Chairman Fred Upton (R-Mich.), who has received more than $12,000 from AT&T executives, employees and their family members. Comcast associates tipped in an additional $10,000 equaling Upton's contribution from the National Cable and Telecommunications Association (NCTA).
And hands aren’t clean on the other side of the aisle either. AT&T, Comcast and NCTA have tipped more than $100,000 into the campaign war chests of Telecommunications Subcommittee Democrats as well.
The corporate largesse is paying dividends. Sources inside the House of Representatives revealed earlier this week that all language pertaining to network neutrality has been struck by subcommittee from the latest draft of the Telecom Act.
According to the National Journal, the Telecommunications Subcommittee is likely to drop all references after lawmakers failed to reach consensus on the issue. If the Journal report is correct, the DC bottleneck is the net result of the full-tilt lobbying by AT&T, Comcast, BellSouth and Verizon.
In addition to the money spent to fill campaign coffers, they have funneled tens of millions of dollars to lobbying efforts, industry friendly think tanks and political junkets, waving a strong hand over all sectors of the political process -- at the local, state and federal levels.
By lining their pockets with telco dollars, certain lawmakers have opted to turn their backs on network neutrality and abandoned their posts as guardians of our public commons. They've decided that committing a crime of omission is better than standing up to the corporate powers that be.
A Telecom Act without network neutrality would hasten the Internet's demise -- effectively ridding our online experience of the governing principle that until now fostered the free flow of ideas and made the Web a beacon for democratic ideas and business innovation.
A Telecom Act without an enforceable rulebook would leave this democratic medium to the whims of predatory telephone and cable companies. The stage is now set for these conglomerates to play gatekeepers to all online content and services -- turning our net freedoms into their net revenues.
If the nation's largest ISPs are allowed to discriminate against the flow of web traffic, The New York Times editorial board wrote on Sunday, "the Internet providers, rather than consumers, could become the driving force in how the Internet evolves."
The profit motive of a few corporations would supplant the freedoms of all users, determining which innovations end up shaping our digital future. The threat is real. These companies could block us from viewing a favorite podcast or blog, cut off net phones unless we use the company service, or force us to download MP3s from their company store while slowing access to other music sites.
AT&T, Bell South, Comcast and Verizon make massive campaign contributions. They're used to getting their way in the halls of Congress. And they don't want network neutrality to stop them from getting their way online.
Only a public outcry can restore this founding principle, before it becomes a footnote in the history of the Internet’s fall.
It's time Americans who feel strongly about an open and free Internet told our elected representatives to reverse course. Net neutrality is an issue where the public's interest cannot be outflanked by massive telcos and their well-oiled politicians.
Monday, January 23, 2006
Why the US Needs a Strong Woman as President
Ok... I'm always willing to take a challenging position on an issue. So here I am stepping into one of the most divisive ones on the approaching horizon. Simply put, I believe the US needs a strong woman as president. Now, I'm not going to say who that woman should be... though for the record, I was a supporter of Elizabeth Dole.
For those of you who missed it, Chile just elected it's first woman president.
Let's start with a few facts:
- There are 7 female presidents worldwide.
- There are 4 female prime ministers.
- 14 women hold spots in the U.S. Senate, 59 women in the House of Representatives and 8 female governors.
The US has already had a woman run for president - just not during most of our lifetimes. The first woman to run for president was Victoria Woodhull in 1872. While most of us have never heard of her, many of the things we take for granted were keys of her platform. She advocated: the 8-hour work day, graduated income tax, social welfare programs, and corporate profit sharing. Woodhull was quite a forward thinker in her time and made few distintions between class and social status. She offered her hospitality to prostitutes and royalty alike. Most considered her a bundle of contradictions. Although she was opposed to the organized Christian religion, she lived its principles: She fed the hungry, cared for the sick, and visited the prisoners. She believed that living those principles was more important to saving souls than preaching the resurrection of Christ. She owned a newspaper which was the first to print the Communist Manifesto in English; and yet, she was also the first female stockbroker on Wall Street. Certianly a strong woman!
More to come...
Tuesday, January 17, 2006
Overheard...
Overheard...
How would you answer that?
How am I going to be true to myself when I have a controlling husband and 4 children who rely on me?
How would you answer that?
Wednesday, December 14, 2005
Is Broadband an Accurate Predictor of Economics
This past week, Indian telecom powerhouse Reliance Infocomm signed a deal with China Telecom establishing a direct cable connection between those two countries. Calls and internet traffic will fly directly over Reliance’s FLAG Telecom cables to connect with China Telecom network in Hong Kong. When compared to meaty issues (such as stopping reauthorization of the {un}Patriot ACT) it doesn’t seem like much, but if you look deeper it could signal longer term fallout on the bandwidth business.
Why? For starters, calls between the two countries untill recently were routed through Europe/US. Now traffic will no longer need to travel half way across the planet. Here in the south, we would have called that going around your elbow to get to your behind. This means reduced role for major US carriers like Level 3, MCI and AT&T (currently the world’s largest ISP... yes, they finally bested MCI/UUnet thanks to the SBC merger). It appears this trend is gathering momentum, and slowly network traffic that almost always used to flow through US is becoming more and more regional. Through most of the 1990s it was cheaper to connect individual European Union (EU) countries through US. In the late 90's and early 2000, small regional networks started to siphon off traffic a country at a time.
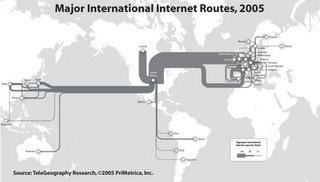 Asia network traffic is following the same trajectory. At some point in the future this is bound to have an impact on the US based carriers. Currently, the US is the top Internet hub country with 1.4 terabits/second of bandwidth. World’s fattest pipes (metaphorically speaking) are between London and New York, about 320 GB/s of bandwidth.
Will the regionalization of the traffic mean price wars will rear their ugly head? Will the prices plunge on the London-New York routes as once again capacity outstrips demand? Some folks who work in the bandwidth business are muttering that the transit fees, that once used to make up nice profit center for global carriers, are beginning to wane. This probably explains at least part of the back story in the flap between Level3 and Cogent over private peering last month. (People don't want pay Level3's rates for transit anymore... they're often seen as too high.)
Looking beyond the obvious - is this a general global economic trend? I won't pretend to know anything substantive about global trade, but my broadband crystal ball (with fresh batteries and all!) indicates that this could be forbearer of a global trade shift. I believe that what oceanic/sea routes, air routes and highways were to the 20th century, broadband pipes are to the 21st century. From that perspective, things could be shifting away from the US being the hub of global trade. [Is that news to anyone on the investment banking sector? I think not!]
(Adapted from Om Malik's Broadband Blog)
Why? For starters, calls between the two countries untill recently were routed through Europe/US. Now traffic will no longer need to travel half way across the planet. Here in the south, we would have called that going around your elbow to get to your behind. This means reduced role for major US carriers like Level 3, MCI and AT&T (currently the world’s largest ISP... yes, they finally bested MCI/UUnet thanks to the SBC merger). It appears this trend is gathering momentum, and slowly network traffic that almost always used to flow through US is becoming more and more regional. Through most of the 1990s it was cheaper to connect individual European Union (EU) countries through US. In the late 90's and early 2000, small regional networks started to siphon off traffic a country at a time.
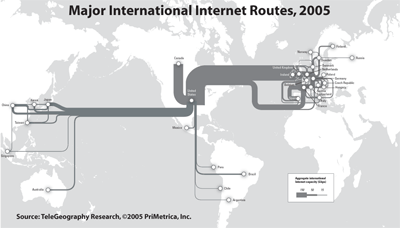 Asia network traffic is following the same trajectory. At some point in the future this is bound to have an impact on the US based carriers. Currently, the US is the top Internet hub country with 1.4 terabits/second of bandwidth. World’s fattest pipes (metaphorically speaking) are between London and New York, about 320 GB/s of bandwidth.
Will the regionalization of the traffic mean price wars will rear their ugly head? Will the prices plunge on the London-New York routes as once again capacity outstrips demand? Some folks who work in the bandwidth business are muttering that the transit fees, that once used to make up nice profit center for global carriers, are beginning to wane. This probably explains at least part of the back story in the flap between Level3 and Cogent over private peering last month. (People don't want pay Level3's rates for transit anymore... they're often seen as too high.)
Looking beyond the obvious - is this a general global economic trend? I won't pretend to know anything substantive about global trade, but my broadband crystal ball (with fresh batteries and all!) indicates that this could be forbearer of a global trade shift. I believe that what oceanic/sea routes, air routes and highways were to the 20th century, broadband pipes are to the 21st century. From that perspective, things could be shifting away from the US being the hub of global trade. [Is that news to anyone on the investment banking sector? I think not!]
(Adapted from Om Malik's Broadband Blog)
Thursday, November 17, 2005
White House Hijacks Patriot Act Reform
ACLU Says White House Usurps Patriot Act Reauthorization Process, Negotiators Neglect Privacy and Civil Liberties Concerns but Add Poison Pills
 WASHINGTON - A conference committee tasked to reconcile differences between House and Senate Patriot Act bills ignored bipartisan calls to restore checks and balances on government power and protect privacy and civil liberties, the American Civil Liberties Union said today. The Republican-led conferees also attached several "poison pill" measures to the must-pass legislation, unrelated to the 2001 anti-terrorism law. The House and Senate are expected to vote on the bill this week.
The following can be attributed to Lisa Graves, ACLU Senior Counsel for Legislative Strategy:
"The Patriot Act was bad in 2001, and despite bipartisan calls for reform, it's still bad in 2005. Instead of addressing the real concerns that millions of Americans have about the Patriot Act, the Republican majority in Congress buckled to White House pressure, stripping the bill of modest yet meaningful reforms. Congress must reject this bill.
"Don't be fooled by some lawmakers spinning this bill as Patriot Act reform. It’s anything but. Lawmakers have let the administration take us from bad to worse. There's a reason why groups like the Chamber of Commerce, American Conservative Union and American Library Association have all come together for Patriot Act reform. The question is: Why haven’t lawmakers listened?"
WASHINGTON - A conference committee tasked to reconcile differences between House and Senate Patriot Act bills ignored bipartisan calls to restore checks and balances on government power and protect privacy and civil liberties, the American Civil Liberties Union said today. The Republican-led conferees also attached several "poison pill" measures to the must-pass legislation, unrelated to the 2001 anti-terrorism law. The House and Senate are expected to vote on the bill this week.The following can be attributed to Lisa Graves, ACLU Senior Counsel for Legislative Strategy:
"The Patriot Act was bad in 2001, and despite bipartisan calls for reform, it's still bad in 2005. Instead of addressing the real concerns that millions of Americans have about the Patriot Act, the Republican majority in Congress buckled to White House pressure, stripping the bill of modest yet meaningful reforms. Congress must reject this bill.
"Don't be fooled by some lawmakers spinning this bill as Patriot Act reform. It’s anything but. Lawmakers have let the administration take us from bad to worse. There's a reason why groups like the Chamber of Commerce, American Conservative Union and American Library Association have all come together for Patriot Act reform. The question is: Why haven’t lawmakers listened?"
Thursday, October 27, 2005
DoD Buying Sprint's iDEN Network
The PCS Intel Blog is running a story that indicates the Department of Defense will be buying Sprint's iDEN network as "the first phase of a national overhaul of its security framework in regards to communication." The gist is that the government will move much of its wireless communications onto one encrypted wireless network, and Sprint/Nextel customers will be issued dual-network CDMA/iDEN handsets, so that as iDEN becomes restricted, CDMA will take its place.
The report also claims that in exchange, Sprint will get plenty of spectrum in the 700 & 800Mhz bands for mobile Wimax broadband service. Keep in mind that if true, most of this wouldn't happen until around 2010, which roughly gels with Wimax analyst timeline predictions. The report claims the deal won't even be announced until 2007 or 2008.
This move makes this week's news of a Sprint co-branding wireless deal with Comcast, Time Warner Cable, and Cox slightly more interesting. The deal would give Sprint priority access to Wimax spectrum, letting those three cable giants offer re-branded Wimax to better compete with baby Bell Wimax offerings.
This whole scenario assumes a lot; at the forefront that mobile Wimax is a solid business model. If Wimax tanks however, the report seems to indicate that Sprint's deal with Uncle Sam allows them to instead grab ample 2.5 GHz spectrum, and deploy the most popular technology at the time (like WiBro).
Either way, the cable industry would be well positioned for wireless broadband competition.
DoD iDEN
The United States of America has come to a fundamental conclusion about its national communications infrastructure post-9/11 in regards to homeland security; it's broken. The Department of Defense, working with the FCC, DHS, the President, and Congress has brokered a framework agreement to purchase Sprint Nextel's iDEN network as the first phase of a national overhaul of its security framework in regards to communication.
The plan is simple; everyone involved in securing this nation will be on the same network. This network will be using an encrypted iDEN sequence, ensuring that all soldiers, first responders, and chain of command will be able to contact each other. This is especially in the event of a series of disasters in concert (say, for example, multiple terrorist attacks in multiple major metropolitan areas simultaneously).
We do not intend to disclose details of the inner-workings or how DoD iDEN will differ from the current iDEN. We will only say that the transition will be announced approximately two to three years from the deprecation date of iDEN at 2010. All Nextel customers will be issued dual-network CDMA/iDEN handsets, so that as iDEN is barred from consumer use, CDMA will take its place.
Sprint WiMax
We are finally ready to disclose Sprint's master plan for WiMax as well. Sprint intends to deploy a national, non-fixed WiMax network with as much, if not more coverage than the existing CDMA network. WiMax will effectively act as a replacement to CDMA data, providing FIOS-like speeds via massive towers that resemble TV towers in major cities.
This will enable Sprint to not only be a national ISP, but to remove common conceptions of fixed ISP. The WIMax modem technology Sprint is attempting to deploy will ensure that a broad range of WiMax devices will share an account... for example, WiMax deployments could fit in a PDA that would share bandwidth allocations with home internet that would share bandwidth allocations with your HDTV.
Sprint intends to compete directly with Cable, Satellite, ISPs, and traditional Wireless. By bundling all telecommunication services ever envisioned, Sprint will tackle everyone by offering everything.
Now, how is Sprint going to get there? Sprint has multiple hurdles it must cross in order to obtain this vision. First, Sprint must gain a WiMax standard. Sprint is doing this by attempting to force WiMax standards through as an open modem technology... one WiMax device is compatible with another, and is mobile from the start. If this fails, Sprint will most likely divert to the nearest derivative of WiMax, currently WiBro, though Flash-ODFM is an additional fallback should such subsequent technologies also fail.
But, Sprint was late to the WiMax game... Sprint lacks the licenses to deploy a national WiMax network on the critical 700 MHz band.
In comes the FCC. As a part of the transaction of iDEN to the federal government, Sprint will gain a blank check to rebuild the 700 and 800 MHz bands in their image, taking licenses as needed from whoever has them regardless of how fairly they gained them at FCC auction in the past. With Congress, the FCC, and the President in the loop, Forsee, Donahue, and Lauer will have no problem in gaining dominance of the WiMax and digital CDMA 800 MHz spectrum needed to reform technologies in their image.
The final step in this strategy is bandwidth. As you may know, local loops to existing cellular structure generally tap out at about 10 T1 lines per tower in a high traffic cell site. Sprint will form a network coalition to utilize dark fiber across the country to connect the city-wide WiMax towers whenever possible, feeding into Sprintlink backbones in order to ensure that the entire network is able to deliver above-DSL speeds to all customers at all times. Clearly, the goal is to make all metropolitan areas at least initially wired via fiber, and eventually, to create a national fiber optics "spine" that will connect every citizen wirelessly to a fiber optics internet directly.
The Rebels Fight Back
We are reporting all of this today, which we have known and been briefed on for an extremely long time, because we have been notified that Sprint's competition, namely WiMax ISP newcomers that you probably have never heard of before, have learned this information above within the past week.
In short, they are flying to Washington D.C. to fight back in Congress and with the FCC. Now aware to these plans, they see that all their technology investments will go to waste if the FCC choses to pull their 700 MHz licenses key to WiMax "in the public interest". While we love a good behind-the-scenes fight, we have been informed this news will become public domain later this week.
Remember, these "rebels" have nothing to lose, and they intend to scream from the highest mountains this in a war between Sprint and Sprint's hardware suppliers, and the rest of the WiMax forum.
Sprint also has options if their plan fails. We have obtained intelligence recently that Sprint will deploy on the 2.5 GHz spectrum if they are unable to obtain sufficient 700 MHz spectrum. However, the inherent advantages of 700 MHz spectrum over 2.5 GHz spectrum, combined with the added ability to strike a major blow to dissent from Sprint’s vision of WiMax makes it a battle well worth fighting to Sprint.
The PR Spin Rooms Are Spinning
"When the United States depends on the power and performance of Sprint's networks, then yes, I guess I am a Yes Man."
- President Bush, circa 2007
Cue the Sprint pin drop, "Sprint, yes you can", etc. Sprint is billing this strategy as one that will secure the nation, and deliver on the President's promise of national broadband internet by 2010. There are many more details that we are aware of, however, in the sake of national security we will not disclose them here. Again, it is important to note that what is disclosed here will become public domain within the week, however, this is clearly a win-win for all parties involved.
The Editorial
I'm sure many of you will ask my personal thoughts on this. Personally, I think it is the most amazing cooperation between corporate, technological, and political facets of society to-date. It will secure the country, and deliver something that no other technological society has ever offered; wireless broadband internet for everyone. It will ensure that every commander can communicate to every single person he or she is in command of, either through the chain of command or directly at any time. It will ensure that the United States will be the leader in wireless communication and national communications security for the next 25 years.
Bring it on.
Tuesday, October 18, 2005
Verizon EVDO: Unlimited, Isn't
Customers receive bandwidth consumption letters
Verizon's EVDO wireless broadband service promises unlimited data consumption, but as usual in this industry - that means the exact opposite. Verizon Wireless had already been complaining about the use of Junxion boxes to split 3G connections. Now, according to posters to the EVDO forums (via Techdirt), they're sending out warning letters (see copy) to users who consume too much bandwidth. We're not sure how many times we have to say this: If you're going to restrict consumption in any way, then don't tag your service as "unlimited".
Verizon's EVDO wireless broadband service promises unlimited data consumption, but as usual in this industry - that means the exact opposite. Verizon Wireless had already been complaining about the use of Junxion boxes to split 3G connections. Now, according to posters to the EVDO forums (via Techdirt), they're sending out warning letters (see copy) to users who consume too much bandwidth. We're not sure how many times we have to say this: If you're going to restrict consumption in any way, then don't tag your service as "unlimited".

Thursday, October 13, 2005
10,000 Midtown NY Phones Dead
A major phone outage in Midtown has left thousands of people without dial tones, and a solution is still days away. Landlines, Internet access and fax machines for many Verizon customers in the area have been shut down since Tuesday after a fire melted cables inside a manhole at 38th Street and Madison Avenue.
Verizon, which doesn't know the cause of the fire, said yesterday that as many as 10,000 customers in both homes and businesses are still without landlines in the heart of the city.
"At this point, we haven't estimated how soon we'll have it [repairs] all done . . . possibly sometime next week," said Verizon spokesman Cliff Lee.
"It's going to be a very time-consuming process, because of the situation and the [underground] location."
To ease the pain, Verizon has placed vans with free phones for the public to use in the affected area and will offer rebates for affected customers. But the outage has business owners fuming as they struggle to operate without fax machines, e-mail or regular phones.
"It's impossible to run a law firm without e-mail and faxes in 2005," said Paul Korngold, a partner at Tuchman, Katz, Schwartz, Gelles, Korngold and Weiss, whose lines have been down since the start of business on Wednesday.
It's still not clear what sparked the manhole fire that caused the problem. Verizon said that by yesterday workers had gotten fiber optic lines working, but they still had to repair melted copper wires.
Friday, October 07, 2005
The Best Geek Quotes
- There are 10 types of people in the world: those who understand binary, and those who don't.
- If at first you don't succeed; call it version 1.0
- I'm not anti-social; I'm just not user friendly
- Roses are #FF0000
Violets are #0000FF
All my base
Are belong to you
- My software never has bugs. It just develops random features.
- My pokemon bring all the nerds to the yard, and they're like you wanna trade cards? Darn right, I wanna trade cards, I'll trade this but not my charizard.
- Microsoft: "You've got questions. We've got dancing paperclips."
- A computer lets you make more mistakes faster than any invention in human history - with the possible exceptions of handguns and tequila.
- I would love to change the world, but they won't give me the source code.
- The box said 'Requires Windows 95 or better'. So I installed LINUX.
Tuesday, October 04, 2005
Health Insurance Search Engine
NEED Health Insurance? In addition to featuring the largest selection of major medical health plans from leading companies, eHealthInsurance also offers a wide selection of quality short term, student, and dental plans. You can obtain FREE instant quotes, side-by-side comparisons, the best available prices, online applications, and a knowledgeable Customer Care team to help you find the plan that is right for you. ShopforT1 revolutionized shopping for T1 and internet circuits. Now eHealthInsurance revolutionizes shopping for health insurance.
Sunday, October 02, 2005
For Verizon VoIP, Unlimited Really Means 5000 Minutes
Verizon VoiceWing fine-print on unlimited plans.
Verizon reserves the right to monitor usage for possible abuse of service. For packages with unlimited calling, more than 5,000 minutes a month is considered beyond normal residential use and may be investigated, resulting in potential termination of service.That’s about 3 hours a day… not a lot of talk time! (Hat Tip, Chris Holland)
Monday, September 26, 2005
VoIP a not quite ready for primetime player
Monday, September 19, 2005
The 'We're Not Taking Any More' club
p2pnet Special:- An unusual, extremely expensive, international online club is starting to form.
Its first member was Patricia Santangelo, a single New York mother of five.
Next came Dawnell Leadbetter, another single mother, this time from the Seattle area. If you’re a regular p2pnet reader, you’ll recognize both of the above names.
 The third member was someone you haven't met before: Tanya Andersen (right), a single mother who's living in Oregon and who's seriously disabled with a painful medical condition. She and her eight-year-old daughter get by on social security payments.
By now, you'll have probably guessed the club members are all women being brutally victimized by EMI, Universal, Warner and Sony BMG, the huge, multi-billion-dollar record label cartel that's using its immense financial and political weight and deep, dark connections to law enforcement agencies in a bizarre marketing scheme.
Instead of wooing customers, it's suing them and so far, it's clocked up close to 14,000 people.
But the significance of the three women isn't that they're among the unfortunate victims.
Rather, they stand out because they're standing up, defying the Mafia-like labels and their teams of hired legal thugs who work through 'Settlement Centers' which aim to terrorize people into paying 'fees' which usually start out at $7,500 to be 'negotiated' down to around $3,500.
Do you think the superlatives victimize, brutal, terrorize and bizarre are too strong?
They're not strong enough.
The We're Not Taking Any More club
Patricia Santangelo was the first to take the labels on, represented by Ty Rogers, Ray Beckerman and Dan Singer of New York’s Beldock Levine & Hoffman.
She tells other victims, "Don't let your fear of these massive companies allow you to deny your belief in your own innocence. Paying these settlements is an admission of guilt. If you're not guilty of violating the law, don't pay."
Dawnell Leadbetter, backed by Lory Lybeck of Lybeck Murphy in Oregon, says she’s not willing to let the labels walk all over her. We'll be running our interview with her within the next few days.
More recently, Tanya Andersen, also represented by Lybeck, has decided she’s not going to put up with Big Music’s bullying either.
"It was something I got in the mail and that I didn't quite understand from them stating they were releasing my private information," she told p2pnet. "They had a subpoena attached and it basically sounded to me when I read it that they were just investigating something and wanted my information.
"I thought, 'Well I haven't done anything wrong so I'm not going to worry about it'."
However, this was far from being an innocuous inquiry. In was the beginning of a nightmare for Anderson. And it's still going on.
The letter she refers to was from ISP Verizon telling her the company was releasing personal information to the Big Four's RIAA (Recording Industry Association of America), fronted by one of the Settlement Centers the enforcement unit uses to do its dirty work.
'I have no money and did not do what is being said'
In a March 6, 2005, letter to Mark Eilers at the Tukwila, Washington, 'Settlement Centre,' Andersen states categorically that neither she nor anyone in her household has ever downloaded "illegal" digital files.
"If somehow this activity was to somehow been pinned to me, it was somehow done so fraudulently," she says. "There is no way it came from my household.
"I have the least expensive computer system you can buy from Dell. The type you order off television for $499.00. It was purchased in the summer of 2002 and has the smallest hard drive they make. I have no cd writer on it and the cd-rom that I do have, does not even work correctly.
"I live alone with my 8-year-old daughter (who would have been seven at the time the alleged occurrence took place). I am a single mom who is disabled and unable to work. I live on Social Security disability and struggle to support my daughter and myself. If I am put in a position where I need to defend myself regarding this situation, it would create extreme financial hardship on me. I have no money and did not do what is being said. I also must admit that all this stuff that has been occurring with this whole ordeal has triggered my medical condition to flare lately.
"I have always been against music downloading. In fact, I have been a member of BMG's music club for quite some time and I purchase my music either from there or from Target. When I first got my computer set up almost three years ago, I had a friend set it up for me since I did not know how to do it. She had put Kaaza Lite on there and told me what it was. I never used it and had no interest in doing so. I deleted it since I had no use for it. Even though I deleted it correctly, as is recommended by Microsoft, Mr. Eilers has told me it can hide out in my system and play without me knowing about it. I have done a total check
of my computer and it is no where on there.
"These files you are speaking accusing me of sharing (which Mr. Eiler told me about), are not and never have been on my computer system. Several of those artists, I have never even heard of! One, I understand, is a rap song. I am 42-years-old and do not even like rap music. The login that this person who did this apparently used, which Mr. Eiler told me of, is not a login name I have ever used or heard of.
"There is no one at my household who could have done what is being said at all. Mr. Eiler had brought up the fact that maybe a babysitter could have done it and that is impossible because I seldom have a sitter since I can't afford to pay one and am usually home."
'Turning her life upside down'
Andersen contacted the recording industry, Verizon, the Settlement Support Center, US congressman David Wu and US senators Ron Wyden and Gordon Smith, "pleading for their help and investigation," her lawyer, Lorry Lybeck, told p2pnet, going on:
"She didn't engage in any copyright infringement nor did she download or share any songs on her computer. After offering to make her computer available to the strong-arming record industry and explaining to them that she could not, and did not, engage in any prohibited conduct, the secret suit was dismissed and she was then sued in her name by another group of large record companies in federal district court in Oregon.
"The continuing victimization of Ms Anderson and the unwillingness of the record companies to conduct even the most basic investigation before turning her life upside down betrays the total lack of concern they have for any concepts of fairness, due process and the rights of the individuals who they have wrongfully targeted.
"If this lawsuit were filed for real purposes of fact finding and a determination of damages owed, the record companies would have been required to undertake a real investigation and determine whether a real basis existed to sue Ms Anderson.
"In this circumstance, the real motivation and purpose of this suit (and the 15,000+ others clogging the federal courts) is to promote a national PR campaign being conducted by the RIAA. Because of this, the 'plaintiffs' in these many suits have no interest in investigating whether facts actually exist to support the allegations in the lawsuits. It is the publication of the threat of the suit that the RIAA wants.
"The federal courts have important business before them. It is an outrage that the RIAA is abusing the federal court system to obtain the ability to threaten many many thousands of American citizens.
"Copyright infringement is wrong. Thug-like threats by multi-national, multi-billion dollar businesses against people who cannot afford to speak or even explain their innonence is a much greater wrong. The music industry with all of its assets and all of its talents has the ability to handle the 'problem' of downloading much more effectively and much more humanely. Their present tactics cause real harm to real people.
"Theses tactics do nothing to address highjackers, spoofers and commercially motivated copyright infringers around the world.
"The RIAA needs to stop hurting innocent people."
Candy, James and John
And now, three more people have joined the We're Not Taking Any More club.
Candy Chan, James and Angela Nelson and John Harless are all from Michigan, all represented by John Hermann and all determined not to cave in to EMI, Universal, Warner and Sony BMG.
Hermann gave us brief breakdowns of each of the three cases:
Priority Records v Candy Chan - US District Court Eastern District of Michigan Southern Division Case No 04-cv-73645-DT Honorable: Lawrence Zatkoff.
Candy Chan herself knows nothing about computers, but she does have a 13-year-old daughter and the RIAA went after her, contending she was indirectly liable for providing a computer to her teenage daughter, who denied doing anything wrong. Chan senior said she didn't know who may have downloaded or exchanged music files. But she said she's seen other kids playing with her daughter's computer after school, or at sleep-overs.
"After taking Ms Chan's deposition, the RIAA moved to add the daughter," Hermann told p2pnet. "I objected, arguing that the daughter was a minor and that they had to appoint a guardian ad litem before for the child before they could proceed.
"In the meantime, I threatened filing a motion for summary judgment on behalf of Ms Chan and they immediately moved to withdraw the complaint against her, which the judge granted."
Mowtown Record Company v James and Angela Nelson - US District Court Eastern District of Michigan Southern Division Case No 04-73646; Honorable: Bernard Friedman.
John Nelson freely admits that when it comes to computers, he doesn't have a clue. The Big Four nonetheless accused him of copyright infringement, ignoring his assurances that not only did he not own a p2p file sharing application, but he didn't even know what it was.
However, Nelson's wife, Angela, operates an in-home day care center with several teenagers as her helpers, with all that implies.
"During the deposition of one of the employees, the teenager testified that although she downloaded many of the songs, she did so with Mr and Mrs Nelson's knowledge and approval," says Hermann.
"Based on the teenager's testimony, the RIAA moved to add Mrs Nelson as a defendant.
"During a second series of depositions, the teenage employee recanted her prior statement and said the Nelson's had nothing to do with the downloading and that she'd wrongfully accused them because she was scared and thought she was going to be in trouble herself unless she blamed them.
"Not surprisingly, the RIAA has tried to threaten her in order to change her testimony, even going so far as to hire a private investigator to try and sign a false affidavit indicating that the Nelson's attorney (myself) was active in suborning perjury."
Elecktra Entertainment v John Harless - US District Court Eastern District of Michigan Southern Division Case No 04-cv-74502;Honorable: Bernard Friedman.
John Harless is someone else whose knowledge of computers is to all intents ad purposes, non-existent. But he does have two teenaged children, aged 16 and 14.
The RIAA says Harness infringed its owners' copyrights and, "Although no discovery has been taken, I've tried to obtain information as to the basis of their claims," Hermann told p2pnet.
"Not surprisingly, they've resisted each and every request, no doubt because they have no information other than an IP address and account number.
"I have an order compelling them to produce a Media Sentry representative for a deposition as to the pre-suit investigative procedures, but to date, they've dragged their heels and haven't complied."
Holding a parent responsible
Fred von Lohmann is the EFF's (Electronic Frontier Foundation) senior staff attorney specializing in intellectual property. He represented Morpheus owners Streamcast Networks in the Grokster vs MGM decision.
“Is it acceptable to make parents responsible in a financial or other sense for something their children may, or may not, have done?” – p2pnet recently asked von Lohmann.
“ The increasing number of lawsuits against the parents and grandparents of alleged file-sharers is a particularly unfortunate part of the recording industry's litigation campaign against music fans,” he said. “There is no precedent in copyright law for holding parent responsible for the infringing activities of their minor children. If the question ever went to court, I believe the RIAA would lose.”
But, “Unfortunately, the RIAA has made it clear that, if a parent fights the lawsuit, they will simply sue the child directly.”
Multi-billion-dollar corporations suing children for sharing music with each other? And sadly, it’s not only in America. The labels are using RIAA clones around the world to run similar terror campaigns aimed at bringing former product 'consumers' to heel.
However, if, in their arrogance, they ever do begin to pillory children, they'll suddenly discover who depends on who.
We'll be running p2pnet Q&As with both Leadbetter and Andersen in the next few days, as well as more details from the individual cases.
If you're a lawyer representing someone else who's joining, the We're Not Taking Any More club, please let us know.
Ditto if you know, or if you are, one of the victims.
Meanwhile -------------
FICTION: File sharers are depriving the music labels (not to mention the movie and software cartels) of billions of dollars in lost sales.
FACT: The cartel is reporting substantial drop-offs in sales and much of this is, its owners claim, down to file sharing.
It's eminently debatable whether file sharing has caused the loss of even a single sale. But the labels have cut back significantly on their output in Australia, say new figures from an Australian expert. Given that it's the case in Oz, one can assume it's also true elsewhere.
There have also been a number of academic and other studies pointing up the fallacy of the cartel assertions.
One of the first to suggest EMI, Universal, Warner and Sony BMG were being a little less than forthright in their 'File sharing is costing us billions in lost sales' declarations came from two respected American scholars.
"According to the RIAA (2002), the number of CD’s shipped in the U.S. fell from 940 million to 800 million - or 15% - between 2000 and 2002 (though shipments continued to rise during the first two years of popular file sharing, 1999-2000)," say Felix Oberholzer of the Harvard Business School and Koleman Strumpf of the University of North Carolina at Chapel Hill in their The Effect of File Sharing on Record Sales: An Empirical Analysis.
"The record industry has claimed this decline is due to file sharing."
The two analyzed the direct data of music downloaders over a 17-week period in the fall of 2002, and compared that activity with actual music purchases during that time, coming to the conclusion that spikes in downloading had almost no discernible effect on sales.
Even under the worst-case example, "it would take 5,000 downloads to reduce the sales of an album by one copy," they wrote. "After annualizing, this would imply a yearly sales loss of two million albums, which is virtually rounding error given that 803 million records were sold in 2002. Sales dropped by 139 million albums from 2000 to 2002."
Nor do downloaded mp3 files replace CD buys.
"While downloads occur on a vast scale, most users are likely individuals who would not have bought the album even in the absence of file sharing," stated Oberholzer and Strumpf.
Their studies concentrated on the American experience. But a more recent study by Dr Tatsuo Tanaka of Keio University in Japan, using the now famous Winny p2p application, says there’s, “not sufficient evidence that file sharing systems are responsible for the recent decline in CD sales”.
To the contrary, p2p usage helps in the promotion of music by allowing users to experience it before purchase; and, it helps in the discovery of new music by users, says Tanaka in Does File Sharing Reduce CD Sales?
"Based on micro data of CD sales and numbers of downloads, we found that there is very little evidence that file sharing reduced music CD sales in Japan. We controlled simultaneous bias between sales and downloads by instrumental variables but did not find correlation between CD sales and numbers of downloads. Although there were large differences in the numbers of downloads among CD titles, these differences did not affect CD sales.
"We also carried out a user survey on file sharing and CD purchases with consideration to the potential bias of respondents trying to understate their illegal copying activity. This survey also showed that file sharing had very limited influence on CD purchases."
Tanaka suggests copyright laws should be relaxed rather than tightened to allow for more positive effects of broadband internet file sharing.
Meanwhile, millions of entertainment industry dollars that should have gone into shareholder dividends are spent on 'reports' meant to counter the papers. But they can be clearly seen for what they are: fruitless attempts to discredit papers which give the lie to industry claims.
FICTION: File sharers are thieves.
FACT: Put at its simplest, to steal something is to remove it from its original owner without his or her permission, causing deprivation through loss. File sharing means exactly what it says. Sharing. Nothing is stolen and no one is deprived of anything. To the contrary, file sharers are exposed to music they may never have otherwise heard. Mp3s are inferior, compressed copies of original CD tracks meant primarily for portable devices. People who listen to mp3s frequently go out to buy the originals so they can be played on home stereo systems.
Moreover, no money changes hands and no profits are made or lost.
FICTION: Targetting people suspected of file sharing has significantly reduced the number of file sharers in the US and around the world.
FACT: The lawsuits have had, and continue to have, zero impact on the file sharing communities. To the contrary, the number of people logging onto file sharing networks everywhere is steadily increasing.
p2pnet has been collecting data compiled by Big Champagne, the American research company which specializes in gathering data on file sharing.
In August, 2003, in the US, on average, 2,630,960 people were simultaneously logged onto p2p networks at any given time. Globally, the number was approximately 3,847,565.
A year later for the same months, the numbers were 4,549,801 and 6,822,312 respectively.
And for August, 2005, Big Champagne statistics show 6,871,308 people were logged onto the networks at the same time in the US, with 9,620,261 individuals checking in around the world.
FICTION: Entertainment industry lawsuits deter people from sharing files with each other online.
FACT: Every day, hundreds of thousands of people around the world log on for the first time meaning the chance of any one individual becoming one of the RIAA's chosen few becomes exponentially more unlikely.
In his Theory of Collective Consumer Risk, "Downloaders are generally less likely to expect a stern warning, expensive lawsuit or even criminal prosecution, the more those around them are doing the same," says Canadian marketing expert Dr Markus Giesler, also quoting p2pnet's contention that the odds of ending up as an RIAA target are akin to being struck by lightning.
Or put another way, the risk tied to Internet file-sharing is almost zero despite entertainment industry claims to the contrary, says Geisler, going on: "Downloaders are generally less likely to expect a stern warning, expensive lawsuit or even criminal prosecution, the more those around them are doing the same."
Slyck is famous for its forums and its statistics. In May this year, "From the last capture of the proportion of networks under the RIAA’s gun in November of 2003, 150 users of FastTrack were sued, compared to 5 Blubster users," said the site’s Tom Mennecke in RIAA’s Grand Total: 10,037 - What are Your Odds?, continuing:
"Since the RIAA cannot subpoena individuals anymore, we unfortunately cannot provide a more current proportion. However, common knowledge dictates that FastTrack remains a priority, and on November 13 of 2003 it represented ~96% of those being sued."
But, "If we were to eliminate 96% (proportion of FastTrack users) of the 6,523 sued in 2004, the odds of being sued changes dramatically. If we consider only those using a non-FastTrack P2P network, the total number of lawsuits drops to only ~261. In other words, you then have a 1 in 45,977 chance of being sued if you do not use FastTrack. Comparatively, according to the National Safety Council, you have a better chance of being killed in a transportation or non-transportational accident, death from suicide, death from assault or death by legal intervention (such as execution or being shot by a police officer.)"
Say, however, half of those sued in 2004 were using FastTrack, that leaves 3,261 non-FastTrack related lawsuits, says Mennecke. "You would then have a 1 in 3,679 chance of being sued. That still places you above all external cases of mortality (1 in 1,755), but below all transportational accidents (1 in 5,953.) However, you would still have a better chance of being killed in an unintentional accident (1 in 2,698), then being sued by the RIAA.
"Although these numbers are hardly an exact science, they do reflect the odds of being sued are little different than the risks one takes by simply living day-to-day life. But if we were to get real specific, the odds of being sued by the RIAA for non-FastTrack users (1 in 3,679) is still much greater than death by contact with a venomous snake or lizard (1 in 95 million.)”
FICTION: Thousands of Americans have been found guilty of 'file sharing'.
FACT: Not one person has ever been found guilty of file sharing, or of anything else. And that's because until Patricia Santangelo came along, not one person had been willing to risk going up against the labels. This in turn has meant no one has appeared before a judge and no alleged case of 'file sharing' has ever been taken to its conclusion.
Worse, the practice makes a mockery of a corner stone of the American legal system: that people are innocent until they're proven guilty.
However, the cartel and their RIAA and other similar industry owned enforcement organizations continue to issue disingenuous press releases suggesting they've successfully prosecuted thousands of 'criminal, thieving' file sharers.
We could go on because pick virtually any aspect of p2p file sharing in music industry statements, and the odds are far better than even that they'll be distortions, if not outright lies, carefully crafted to give the appearance that the labels are beleaguered corporate citizens doing their honest best to survive in a world where millions upon millions of file sharing thieves get up every morning, bent on robbing the labels of what's rightfully theirs, depriving their contracted artists of their livings and causing terrible hardship to support workers.
The contention is obvious nonsense. Nonetheless, the mainstream media repeat these "facts" as though they're a genuine reflection of what's occurring, and as though they come from credible and reliable sources.
And while the labels and their counterparts in the movie and software industries do their best to imitate King Canute in his attempts to turn back the tide, the p2p networks have become a permanent part of the online scene, solidly locked in.
Peer-to-peer is here to stay and as British ISP network service CacheLogic says in a just-published report, p2p not only represented 60% of Net traffic at the end of 2004, it “outstrips every other communication and distribution protocol and is still growing”.
Moreover, p2p and broadband are mutually compatible forces, each driving the uptake of the other, says the report.
The old-style monopolies are slowly but surely being broken down, but it'll take a while before the technologically ignorant executives who run the cartels are replaced by people able to function effectively and profitably in the digital 21st century.
The tragedy is: until that happens, people such as Patricia Santangelo, Dawnell Leadbetter and Tanya Andersen will continue to be persecuted.
And for absolutely nothing.
Stay tuned.
Jon Newton - p2pnet
Subscribe to:
Posts (Atom)